DKIM verification
A rule that adds a subject tag, a banner or a disclaimer changes the message, and a DKIM signature no longer verifies after that. A filter that checks DKIM after the milter, such as Amavis on Zimbra, then takes a valid signature for a broken one.
With DKIM verification on, the milter verifies the DKIM signatures of every message before any rule changes it. It writes the result to an Authentication-Results header, and the DKIM result condition lets the rules act on it.
Open DKIM Verification in the Settings section of the navigation. The page is available to administrators only. DKIM verification is off by default.
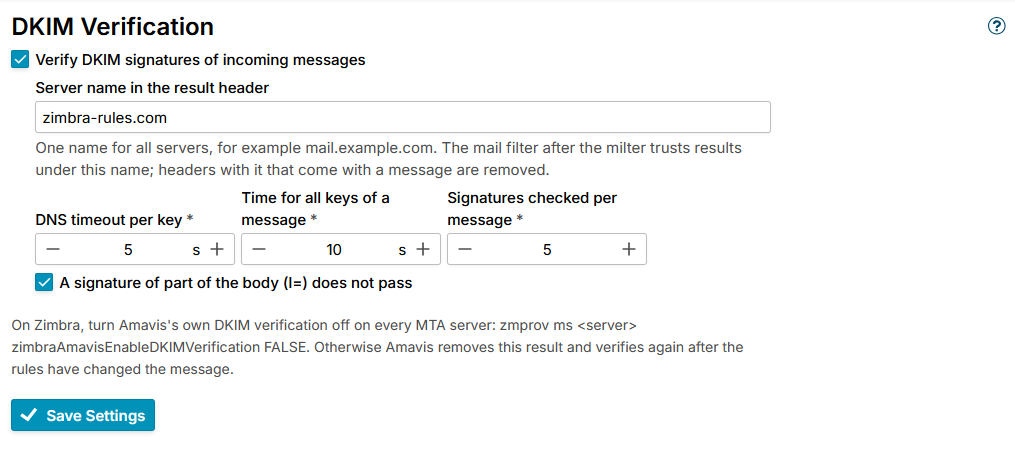
Settings
| Field | Default | Meaning |
|---|---|---|
| Verify DKIM signatures of incoming messages | Off | Turns the verification on. While it is off, the other fields cannot be changed. |
| Server name in the result header | The host name of the first server | The name the results are written under, one name for all servers, for example mail.example.com. The mail filter after the milter trusts results under this name. |
| DNS timeout per key | 5 s | How long the lookup of one key may take, 1 to 30 seconds |
| Time for all keys of a message | 10 s | How long the lookups of all keys of a message may take together, 1 to 60 seconds |
| Signatures checked per message | 5 | How many signatures of a message are verified, 1 to 20 |
| A signature of part of the body (l=) does not pass | On | A signature with l= covers only the start of the body, so content can be appended behind it and the signature still verifies. When on, such a signature does not pass. |
Click Save Settings. The servers pick the settings up with the other settings, usually within a minute.
Amavis on Zimbra
Amavis on Zimbra verifies DKIM too, after the milter. It would remove the result of the milter and verify the message again, after the rules changed it. Before you turn DKIM verification on, turn Amavis's own DKIM verification off. On a single server run this once; with several servers run it on each MTA server, as zmprov gas mta lists them. $(zmhostname) resolves to the host you run it on:
sudo su - zimbra -c 'zmprov ms $(zmhostname) zimbraAmavisEnableDKIMVerification FALSE'
SpamAssassin verifies the signatures again as well, so Zimbra's DMARC rules can still score a message a rule changed as failing. DKIM configuration adds the SpamAssassin rules that take the result of the milter instead, on a single server or on every MTA server.
Additional resources
- DKIM result - the condition that tests the result
- Rules tester - try the condition with a simulated DKIM result