Directory service
The Directory Service page syncs users, groups and domains from Zimbra's built-in OpenLDAP. Once synced, users and groups become available throughout the application - you can use them when defining rule conditions to match messages by sender or recipient, and their attributes fill the placeholders in signature templates.
The sync is multi-domain: every mail domain found in the directory is imported, together with its users and groups. The results are browsable on the Domains page.
Aliases are imported as well, from the zimbraMailAlias attribute, for accounts and for distribution lists alike, and are listed on the user's and the list's page. Account aliases let the Message sender and Message recipient conditions match a message sent to or from an alias as if it used the primary address. List aliases work the same way for the Group option of both conditions, which matches a message addressed to, or sent from, the list itself.
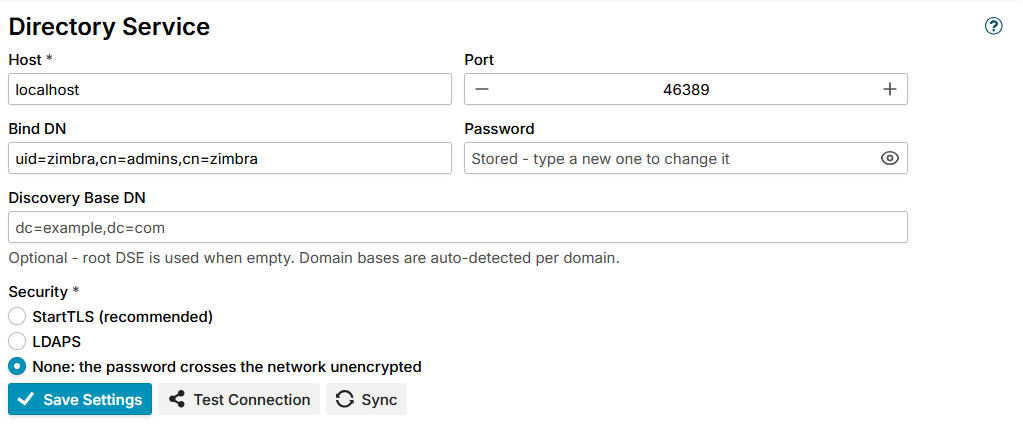
Connection settings
Bind with Zimbra's own LDAP account uid=zimbra,cn=admins,cn=zimbra - the recommended account for this sync. It can filter accounts by zimbraAccountStatus and read the photo attribute for the {photo} template variable; a restricted, read-only application account cannot read either.
Recommended configuration (example for the mail domain ubuntu.lan on the Zimbra host mx.ubuntu.lan):
| Field | Example value | Command to obtain the value |
|---|---|---|
| Host | mx.ubuntu.lan | sudo su - zimbra -c 'zmlocalconfig -m nokey ldap_host' |
| Port | 389 | sudo su - zimbra -c 'zmlocalconfig -m nokey ldap_port' |
| Bind DN | uid=zimbra,cn=admins,cn=zimbra | sudo su - zimbra -c 'zmlocalconfig -m nokey zimbra_ldap_userdn' |
| Password | The password of Zimbra's LDAP account | sudo su - zimbra -c 'zmlocalconfig -s -m nokey zimbra_ldap_password' |
| Discovery Base DN | Leave empty, or dc=ubuntu,dc=lan | None needed when empty. For one domain, see below. |
| Security | StartTLS (recommended) | sudo su - zimbra -c 'zmlocalconfig -m nokey ldap_starttls_supported' - 1 means Zimbra's LDAP offers StartTLS |
Run the commands on the Zimbra server, or on any of them in a multi-server installation: every Zimbra server knows its LDAP. Each prints only the value, ready to paste into the field. The password needs -s, otherwise zmlocalconfig hides it.
Discovery Base DN
Discovery Base DN is optional. When it is empty, the sync starts from the LDAP root DSE and discovers all mail domains automatically; the base DN of each domain is auto-detected. Set it only when you want to restrict the sync to a single subtree - a mail domain example.com maps to the base DN dc=example,dc=com (each dot becomes a dc= part). This command prints the base DN of every mail domain, one per line; pick the one of the domain you want to sync:
sudo su - zimbra -c 'zmprov -l gad' | sed 's/^/dc=/; s/\./,dc=/g'
Security
Security decides how the connection to the directory is protected. MSH Zimbra Rules binds only once TLS is up, so the bind DN and the password never cross the network in clear with StartTLS or LDAPS.
| Security | Port | Meaning |
|---|---|---|
| StartTLS (recommended) | 389 | Connects to the usual LDAP port and switches to TLS before the bind. Zimbra's LDAP offers it as installed. The default for a new connection. |
| LDAPS | 636 | Connects with TLS from the start. Zimbra does not listen on 636 unless it was set up. |
| None: the password crosses the network unencrypted | 389 | No TLS. Use it only for a directory without TLS. |
When you change Security while the port is still the default of the previous choice, the port changes with it.
Trusting the certificate of the directory
Zimbra's LDAP certificate is signed by Zimbra's own certificate authority, which Java does not trust. The first Test Connection then opens the dialog The certificate of the directory is not trusted, with the subject, the issuer and the SHA-256 fingerprint of the certificate.
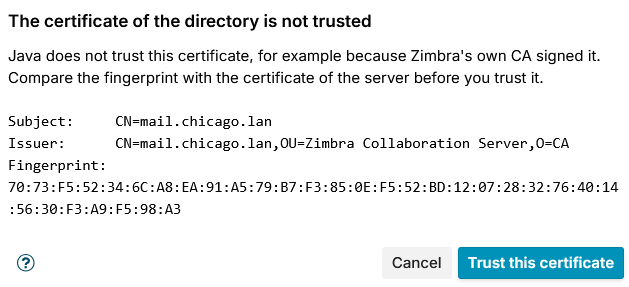
Compare the fingerprint with the certificate of the server before you trust it. On the Zimbra server running the LDAP, this prints the fingerprint in the same form as the dialog:
sudo su - zimbra -c 'openssl x509 -noout -fingerprint -sha256 -in /opt/zimbra/conf/slapd.crt'
If they match, click Trust this certificate, then Save Settings to keep it. The page shows Trusted certificate (SHA-256) with the fingerprint, and from then on only that certificate is accepted. Forget removes it.
When the certificate is renewed, Test Connection opens The certificate of the directory changed with the new certificate and the one trusted so far. Trust the new one only if you know why it changed.
Automatic sync
Sync saves the settings and runs a synchronization at once. The result shows how many domains, users and groups were synced; a failed sync shows More details... with the full error.
The directory sync also runs on its own twice a day, at 00:00 and 12:00 server local time, so the cached domains, users and groups do not go stale between manual runs. A scheduled run is skipped while no host is configured. If the directory server cannot be reached when a run is due, the attempt is logged and not retried - the next attempt is simply the next scheduled time.
Notes
- The user sync includes accounts with status
activeorlocked- a locked account still receives mail, only its owner cannot log in. Accounts with statusclosed,maintenance,pendingorlockoutare left out. - Zimbra's system accounts (
admin@,galsync@,spam.*,ham.*,virus-quarantine.*) are excluded, since they carryzimbraIsSystemAccountorzimbraIsSystemResource. - Calendar resources (rooms, equipment) are excluded as well - they are
zimbraCalendarResourceobjects, not user mailboxes.
Additional resources
- Domains - browse the synced domains, users and groups
- Troubleshooting: Directory service - how to diagnose missing users, groups or attributes